ይህ ገጽ ገና ወደ አማርኛ አልተተረጎመም። የእንግሊዝኛው ጽሑፍ ቀርቧል።
Role-Based Access Control (RBAC) Overview
Enterprise governance framework for SmartERP, business roles, Segregation of Duties (SoD), time-bound access, and immutable audit logging.
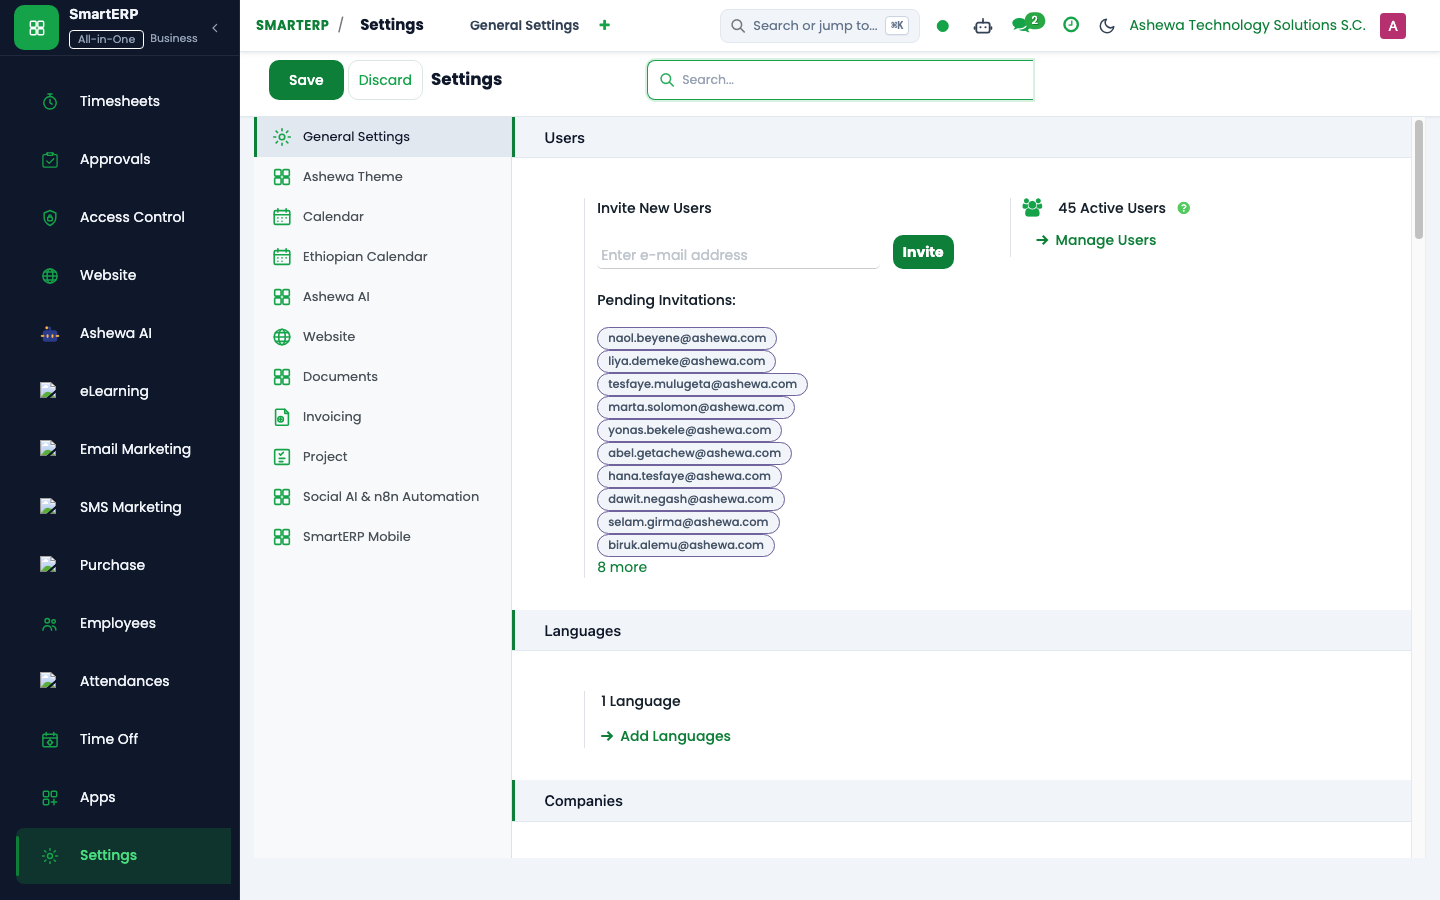
SmartERP Enterprise RBAC (smarterp_rbac) provides enterprise security architecture, replacing unstructured group assignments with governed business roles, automated request workflows, and toxic permission prevention.
Why Enterprise RBAC?#
In standard ERP implementations, administrators assign raw system groups directly to user accounts. Over time, permission creep leads to severe governance risks:
- Former employees retain elevated permissions.
- Toxic combinations (e.g., creating vendors AND approving payments) go undetected.
- Audits fail due to lack of historical justification logs.
SmartERP Enterprise RBAC resolves these challenges through four foundational pillars:
| RBAC Pillar | Technical Subsystem | Governance Benefit |
|---|---|---|
| Governed Business Roles | res.users.role, smarterp.rbac.pack | Bundles technical access into coherent job profiles (e.g., "Junior AP Accountant"). |
| Self-Service Access Requests | smarterp.rbac.request | Automated approval routing with manager endorsement before rights are granted. |
| Segregation of Duties (SoD) | smarterp.rbac.sod.rule | Real-time prevention of toxic permission pairs with hard blocking or audit warnings. |
| Tamper-Evident Audit Trails | smarterp.rbac.audit | Immutable logs capturing who granted what, when, why, and under whose authority. |
Core Application Menus#
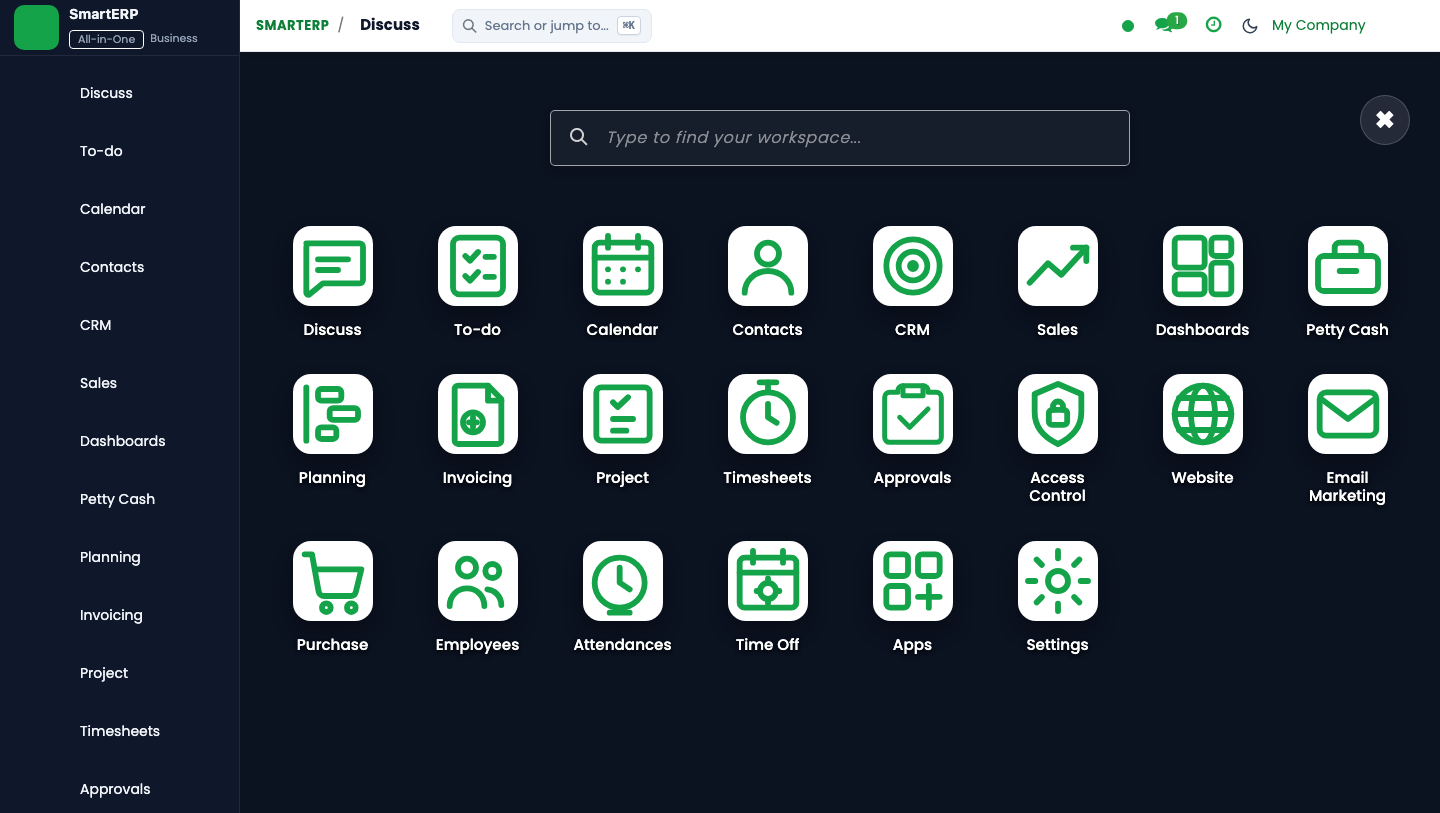
- Settings -> Technical -> RBAC -> Business Roles: Definition of enterprise role profiles and permission packs.
- Settings -> Technical -> RBAC -> Access Requests: Employee request queue and multi-tier approval tracking.
- Settings -> Technical -> RBAC -> Segregation of Duties: Configuration of conflicting role matrices and exceptions.
- Settings -> Technical -> RBAC -> Delegations: Time-bound delegation of authority during leaves.
- Settings -> Technical -> RBAC -> Audit Log: Immutable event ledger of all privilege lifecycle operations.
መጨረሻ የተሻሻለው: 2026-10-16